 23-10-2026
Best Web Portal Development methods are also based on the application of certain security methods to ensure that the information is kept safe from any form of leakage and that access is controlled. This includes Role-Based Access Control (RBAC), where the permissions granted will be dependent on the role an individual plays in the firm. Through this approach, it becomes possible for organizations to manage the access to their systems in an effective way. Web portals can be developed through the use of the above methods.
Understanding Role-Based Access Control in Web Portals
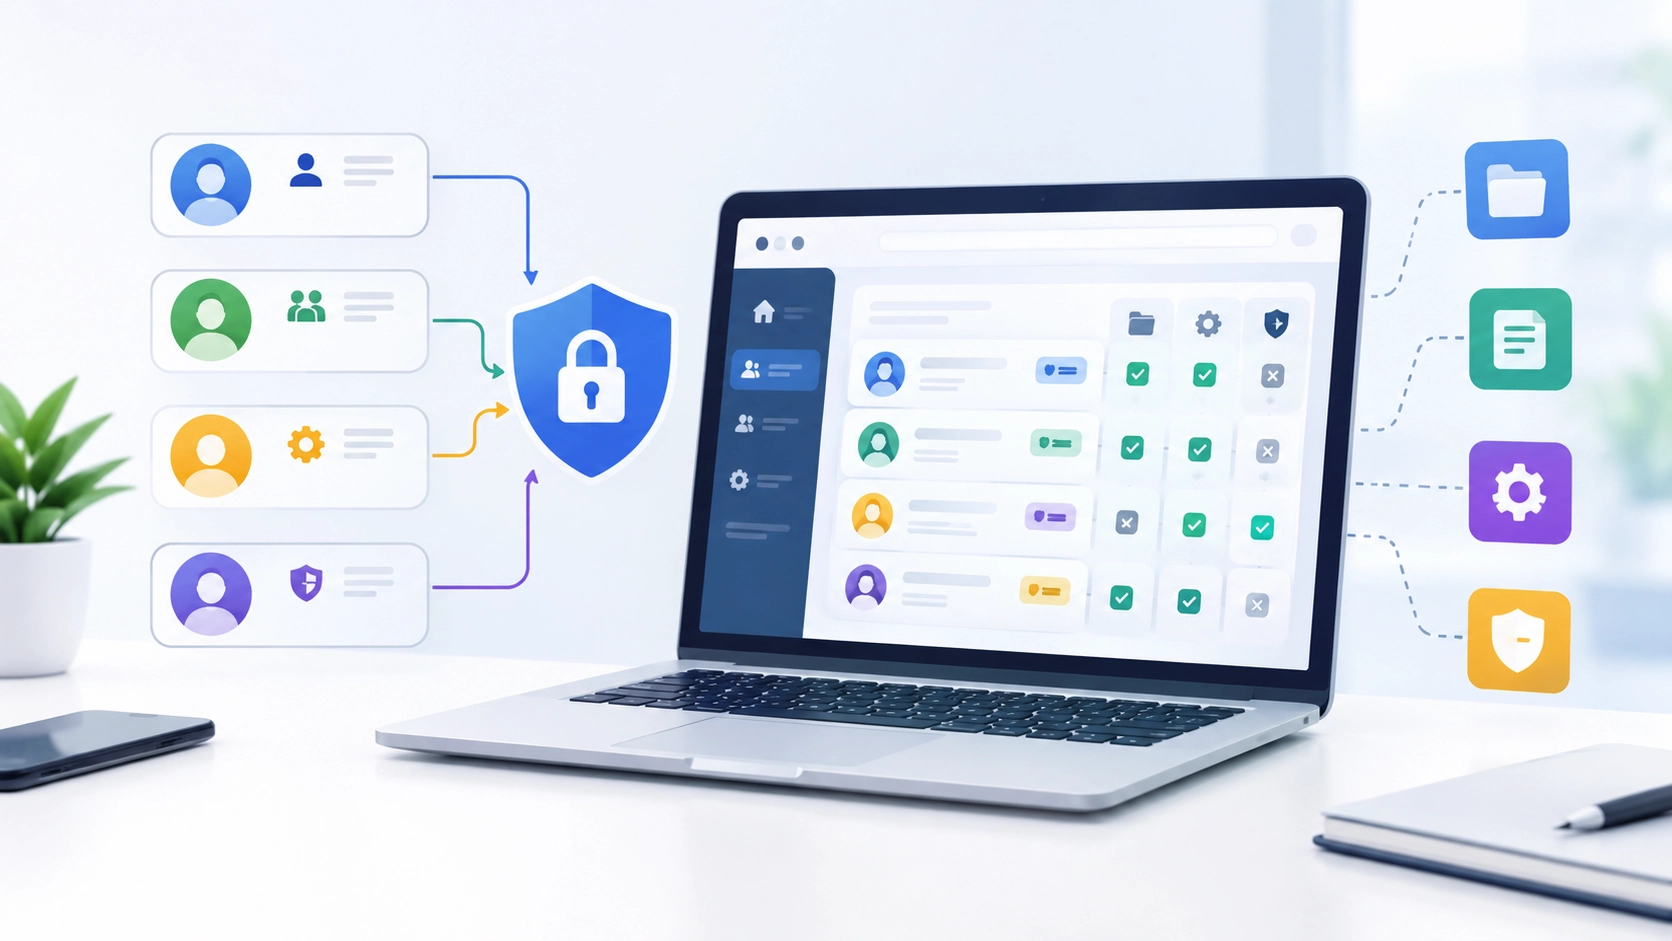
Under Role-Based Access Control, administrators grant some particular permissions to particular roles instead of managing the permissions of each user individually. In that case, the administrator can manage the permissions of users and system configuration, while the employee can access only those features that are required for his work.
The Secure Web Portal Development approach uses Role Based Access Control in order to provide confidentiality of information, manage permissions, and make the process more efficient. The first thing that a developer has to do is create user groups and understand what the responsibilities are and what capabilities each role has.
Steps to Develop an RBAC System
Role-based access control is something that can be accomplished through systematic software development.
Identification of User’s Roles
Determine the roles that the users have within the portal system like administrators, managers, employees, and clients among others. Be sure to specify their roles clearly.
Permissions
Specify what the user is permitted to do, like viewing records, editing data, approval of requests among others
Database Design Structure
Design database tables for users, roles, and permissions and their relationship. A well-structured database will make it easier to manage permissions.
Access Control Implementation
The logic should check if a user is allowed permission access to specific pages, APIs, or functions on the server side. The hiding of the button itself will not suffice.
Testing of Access Rights
Perform tests on different user accounts in order to guarantee appropriate permissions.
Essential Security Practices for RBAC
An RBAC system that is implemented in a secure manner does not simply involve the role assignment. Some of the security considerations to take into account include:
- Least privilege: Give users only those permissions that they require to carry out their duties.
- Permission validation: Validate all permissions at the server side before granting access to protected actions.
- Secure authentication: Secure passwords and implement multi-factor authentication when needed.
- Logging: Maintain logs for any important activity, permission changes, or administrative activities.
- Access reviews: Clean up any unnecessary permissions in case a user is transferred out or quits.
This would help to secure information and improve accountability on the portal.
Benefits of Professional RBAC Implementation
Implementation of an RBAC system properly would guarantee security, efficient management, and expansion of the organization. It also increases the flexibility of adding new roles and permissions into the system without redesigning the whole portal.
Choosing the Best Custom Web Application Development method is beneficial for the organizations to be able to create scalable access control systems according to their requirements. The experts can implement the RBAC system in their databases and authentication systems.
In Webriderz Services Pvt. Ltd., the firms can explore the possibilities of web development which will be focused around the concepts of security, efficiency, and usability. It is possible for the firms to create a website for themselves which will provide them with a secured environment for working in an effective manner.